
Problem first: why this matters
Fleets leak value fast when security and access control are weak. For teams running oil and gas operations, a missing gate, an open telematics port, or a poorly set password invites fuel loss and privacy breaches. I’ve seen field reports where trucks were siphoned overnight near the Gulf of Mexico; those cases show how small gaps become big losses. If you manage oil and gas fleet management, start by treating access control and telemetry like cash—not just data; add a proven fuel theft prevention system where it fits.
What usually breaks
Problems come from three places: human error, weak devices, and bad processes. Humans leave keys or PINs exposed; devices use default credentials or old firmware; processes lack clear roles and logs. Each failure makes theft, spoofing, or unauthorized access easier.
Quick checks you can run today
Do these simple checks right away: verify all vehicle telematics use unique credentials; confirm firmware is up to date; audit who has physical keys and digital access; check logs for repeated failed logins; test emergency override procedures. Mark any item that fails and fix it before the next shift.
Concrete fixes that stop repeat problems
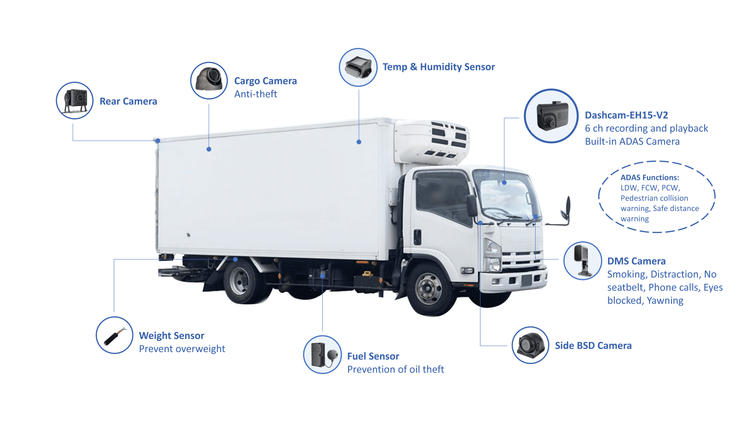
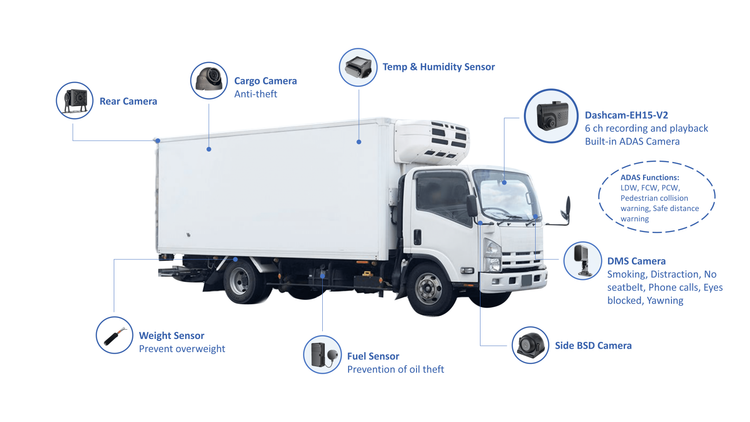
Apply layered controls: enforce multi-factor for admin access; segment the network between onboard systems and maintenance tools; encrypt stored data; require signed firmware updates; use role-based access so drivers can’t change critical settings. Hardware locks, sealed fuel caps, and tank-level sensors add physical deterrence alongside digital controls.
Common mistakes teams keep making
Teams often assume one tool solves everything. They rely only on GPS tracking without tank-level verification; they approve blanket vendor access; they omit routine audits. Those choices look cheaper but invite repeat incidents. Regularly review who can access what, and tie access to a specific, auditable task.
How to evaluate solutions
Compare options on three clear criteria: measurable detection, tamper resistance, and audit trails. Prefer systems that give timestamped tank-level reads, alert on suspicious fill/drain patterns, and produce concise incident reports. Check vendor transparency on data handling and ask for field references; real proof beats glossy demos.
Final synthesis
Start with the problem, fix the simplest gaps, then add controls that scale. Practical steps reduce theft and preserve privacy: unique credentials, signed firmware, segmented networks, and clear roles. Field work shows success when teams measure tank levels, log every access, and treat telemetry like money; that approach is the practical backbone I see delivered by BSJ.